SOCpedia Blog
Monitoring of Linux boot, reboot, and shutdown
1. Problem statement. As part of fulfilling regulatory requirements, it was necessary to prepare an evidentiary base for auditors regarding monitoring of Linux operating system bo…
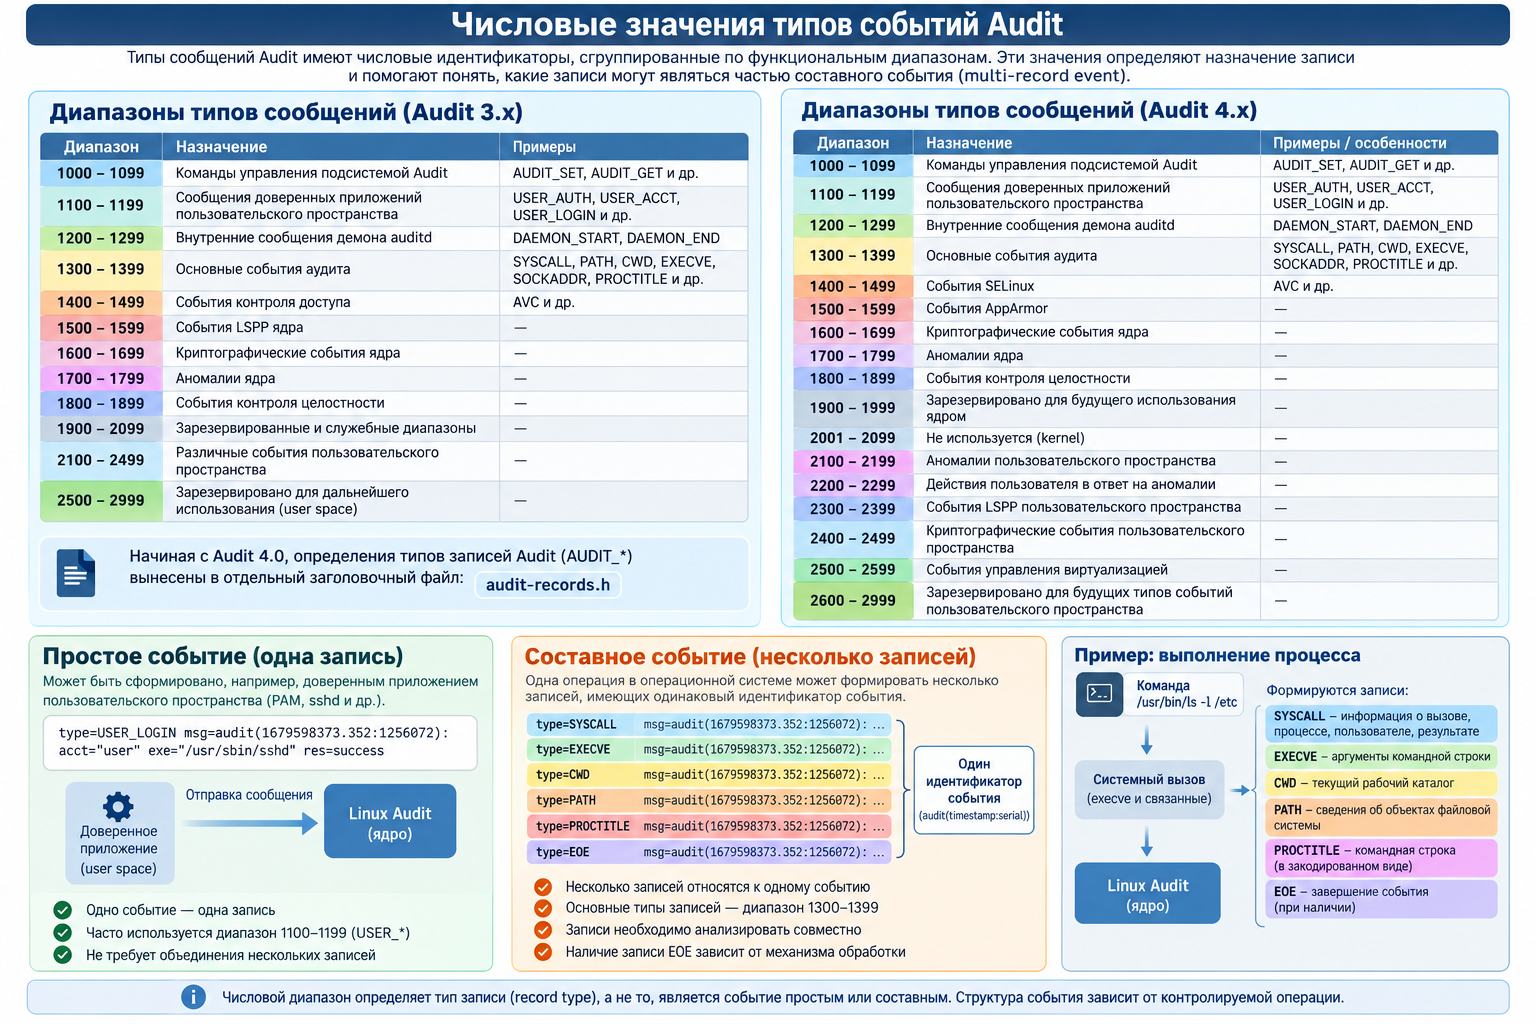
Numeric values of Audit event types
Audit message types have numeric identifiers grouped by functional ranges. These values are important not only for determining a record's purpose, but also for understanding which…
Basic description and architecture of auditd
1. Architecture overview. Linux Audit is an audit subsystem built into the Linux kernel, designed to record events related to the security of the operating system. It allows track…
Security Log Event 4741. How to Detect Suspicious Computer Account Creation in Active Directory
1. Legitimate activity. Event «A computer account was created» (A computer account was created) is generated on the domain controller each time a new computer object is created in…
ShieldBreak – description of the exploitation mechanism for a SOC analyst
ShieldBreak is a local privilege escalation chain to NT AUTHORITY\SYSTEM, claimed by the author to be a bypass of the fix for CVE-2026-50656 (RoguePlanet) in Microsoft Defender. F…